RAPID + TCT 2025: Defense Supply Chain, CMMC, and Additive Manufacturing
VioletX attended RAPID + TCT in Boston — the premier event for additive manufacturing and industrial 3D printing. Here is what we heard on the floor about defense supply chain compliance, CMMC enforcement, FedRAMP, and ISO 9001.
Published May 1, 2025 by Megan Fulton.
Framework: CMMC
Category: Events
What you’ll take away
- Where Additive Manufacturing Meets Federal Compliance
- What We Heard on the Floor
- The Compliance Gap in Additive Manufacturing
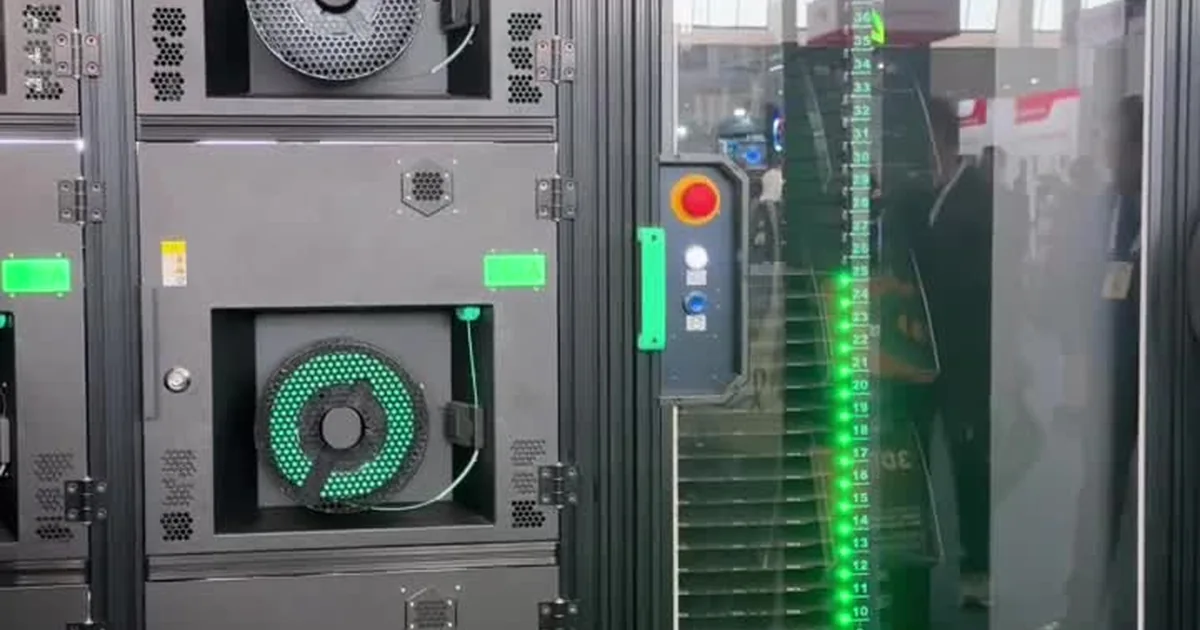
Where Additive Manufacturing Meets Federal Compliance
Additive manufacturing has rapidly moved from prototype labs into active defense supply chains. At RAPID + TCT, that shift was impossible to ignore. Conversations on the floor and in the sessions kept returning to the same tension: speed of innovation versus the rigor of federal compliance requirements.
For companies supplying parts, materials, or software to the Department of Defense, that tension is not academic. It is a contract risk. CMMC, FedRAMP, and ISO 9001 requirements are now table stakes for anyone hoping to remain in or enter the defense industrial base.
What We Heard on the Floor
The conversations VioletX had at RAPID + TCT fell into three recurring themes:
- Defense supply chain pressure: Prime contractors are pushing CMMC requirements down to their suppliers faster than most small and mid-size manufacturers anticipated. Companies that assumed they had another year or two are finding out otherwise.
- FedRAMP as a gateway: Cloud-hosted manufacturing software platforms, including simulation tools, process management systems, and digital twins, are increasingly required to meet FedRAMP standards before DoD procurement will consider them.
- ISO 9001 as the floor, not the ceiling: Quality management certification is now expected as baseline. The more advanced manufacturers are asking how ISO 9001 integrates with their broader security and compliance posture, not treating them as separate programs.
The Compliance Gap in Additive Manufacturing
Many additive manufacturing companies are extraordinary at engineering and extraordinarily unprepared for federal compliance. The capabilities are there. The documentation, evidence collection, policy infrastructure, and audit readiness often are not.
VioletX works with manufacturers and technology companies in exactly this position: technically excellent organizations that need a trusted partner to build and operate the compliance infrastructure required to compete for and retain government contracts.
Frameworks in Focus at RAPID + TCT
- CMMC (Cybersecurity Maturity Model Certification): Required for any contractor handling Controlled Unclassified Information (CUI). Level 2 compliance is now actively enforced across the defense supply chain.
- FedRAMP: The federal standard for cloud service providers. Increasingly relevant as manufacturing software moves to cloud-based platforms.
- ISO 9001: The international quality management standard. Foundational for aerospace and defense supply chain qualification and often a prerequisite for larger defense contracts.
What Comes Next
The manufacturers who will win in the defense market over the next five years are building their compliance programs now, not when a contract is on the line. The companies at RAPID + TCT asking the right questions are the ones who understand that trust is built before it is needed.
If your organization is navigating CMMC, FedRAMP, or ISO 9001 and you want a team that operates compliance as infrastructure rather than a checklist, we should talk.
Related resources
- Vx Federal Platform — Our software platform for federal compliance. FedRAMP, CMMC, and NIST 800-53 operated end-to-end.
- CMMC Compliance — Registered RPO. Zero failed assessments across defense contractors.
- FedRAMP Authorization — Operated authorization programs for cloud providers entering the federal market.