Commerce moves fast. Trust has to keep up.
Security and compliance for the people building the next generation of retail and consumer health—where digital experiences, sensitive choices, and a long partner chain meet.
What matters now
Map customer information across discovery, loyalty, checkout, subscriptions, returns, and support. Connect vendor reviews to decisions and owners. Consumer health requires careful data minimization, disclosures, and partner oversight.
Regulatory scope depends on the organization, products, data, and role. HIPAA does not automatically apply to every consumer health brand or app; other federal or state requirements may be relevant.
Where the industry is heading
Personalization and connected customer journeys make data inventories, permissions, and retention decisions important. AI adoption needs permitted-data rules, human oversight, and a review path. Evidence, named owners, and repeatable response connect policies to operations.
NIST AI Risk Management Framework · FTC Health Breach Notification Rule guidance. Applicability is fact-specific; this briefing is not legal advice.
The work VioletX does
- Application and API security testing
- Cloud security review
- Vendor risk assessments
- Data policies and AI governance
- Managed security and compliance operations
- Security and compliance advisory
Scope is confirmed with your team. No testing begins without agreed targets and authorization.
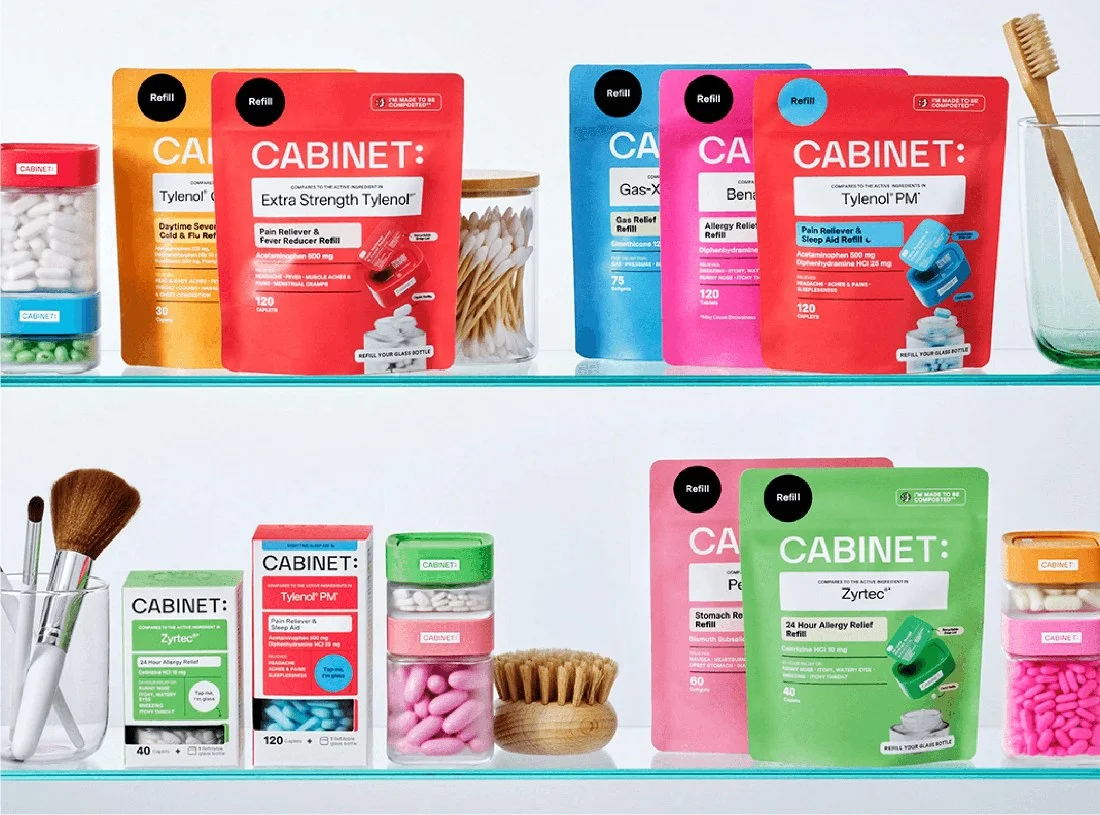
Cabinet Health customer story
VioletX supported Cabinet Health with annual application penetration testing and an AWS infrastructure review, with prioritized security and infrastructure recommendations.
Start a working brief · Browse services · Explore industries